Configuring MCP servers for your organization
Organization admins can enable, configure, and manage MCP server integrations for their entire organization. Once configured at the organization level, agent creators can connect these integrations to individual agents without needing to set up credentials themselves.
The Connectors hub is also where the expanding catalog of 200+ connectors appears as it reaches your organization. For an overview of early availability and progressive rollout, see MCP servers overview.
Accessing MCP server settings
- Navigate to Organization > Connectors in the left sidebar, or go directly to
https://devs.ai/org-connectors. - The Connectors page lists available integrations, including the broader catalog when it is enabled for your organization. The page also shows any custom servers you have created.
From this page, you can:
- Browse and enable pre-built integrations from the catalog
- Create custom MCP server connections
- Finish sign-in or API-key setup for connectors that still need configuration
- Edit or delete existing connections
- Control which connectors are available in agent chat
- See which integrations are connected, ready to use, or still need setup
Enabling a pre-built integration
The platform provides ready-to-use templates for popular services such as Slack, Google Calendar, Gmail, Jira, and many others. As the broader catalog rolls out, you will see additional connectors in the same hub.
- On the Connectors page, browse the list of available templates.
- Click Enable on the integration you want to set up. Ready-to-use connectors open a compact enablement flow: required configuration appears when needed, while Configure keeps optional settings within reach.
- Configure authentication (see Authentication Options below).
- When the connector offers a choice, specify whether each person connects their own account or the organization shares one connection for everyone.
- Review tool permissions (see Tool permission groups below) and select the tools your organization needs.
- Click Save.
Newly enabled connectors default to being available in chat; existing Enable in Chat preferences (the organization toggle on each connector) are preserved when you edit a connector. Managed connectors no longer ask for an unnecessary server URL when the platform already has what it needs.
Once enabled, the integration becomes available for agent creators in your organization to connect to their agents, and members can select it for chat when it is enabled for chat.
Some connectors also pair with products on the AppDirect marketplace. When that applies, you can buy or subscribe to the app on a marketplace and complete the connection in Connectors.
📝 Note: The expanded catalog is early availability and rolls out progressively. If a connector you expect is missing, it may not be enabled for your organization yet.
Creating a custom MCP server
If you need to integrate with an internal system or a service that does not have a pre-built template, you can create a custom MCP server connection.
- On the Connectors page, click Create Custom.
- Enter a Server Name to identify the connection.
- Provide the Server URL — the endpoint where your MCP server is running.
- Optionally upload a Logo to make it easier to identify.
- Choose an authentication type and complete the guided steps (for many servers, especially OAuth, the product detects what is needed and fills in fields for you).
- Click Save.
After saving, the platform connects to your MCP server, discovers available tools, and lists them for you. You can then select which tools to make available.
📝 Note: Custom MCP servers must be accessible over HTTPS. Only URL-based (remote) MCP servers are supported — local or stdio-based servers cannot be connected directly.
Authentication options
When configuring an MCP server, you choose how the platform authenticates with the external service.
OAuth (streamlined setup for custom MCP)
When you connect a custom MCP URL, Devs.ai can usually detect OAuth requirements from the server and walk you through setup in a few steps:
- OAuth is auto-detected from the MCP endpoint where the protocol exposes it.
- OAuth clients can register dynamically (dynamic client registration), so you often avoid copying a Client ID and Client Secret out of a vendor console.
- Fields auto-populate when the server and flow allow it—follow the on-screen prompts as the source of truth for your connection.
- Tokens and tool calls are handled more safely, including stronger protections against unsafe server-side requests when tools run.
For many MCP servers, that means connecting in a few clicks instead of a long manual configuration. If your server or security policy still needs static OAuth app credentials, the UI will ask for them when required.
OAuth (pre-built templates and provider-specific guides)
Pre-built integrations (Slack, Google, Atlassian, GitHub, Dropbox, and others) still follow each vendor’s expectations. Often you will create an OAuth app in the provider’s console and paste Client ID and Client Secret into the connector, because the template is tied to your organization’s app registration.
With OAuth in general:
- Each user authorizes access to their own account the first time they use the integration (where the flow is per-user).
- The platform stores and refreshes tokens securely.
- Setup is more reliable than in earlier releases, including automatic PKCE where the provider requires it.
For step-by-step OAuth setup, see the individual server pages:
- Slack
- Google Services (Calendar, Gmail, Drive, Docs, Sheets, Slides)
- Jira & Confluence
- GitHub
- Dropbox
API key
For services that authenticate using a static API key:
- Select API Key as the authentication type.
- Enter the API key value.
- The key is encrypted and stored securely by the platform.
Pass-through headers
For internal services that accept the same credentials your users already send to Devs.ai (such as SSO tokens or internal API keys):
- Select Pass-Through Headers as the authentication type.
- Configure which headers should be forwarded to the MCP server.
For more details, see Pass-through headers authentication.
None
For MCP servers that do not require authentication (for example, public or internal endpoints on a private network).
Managing connectors
The Connectors hub makes it clearer where each integration stands. Typical statuses include:
- Connected — Authentication is in place and the connector is usable.
- Ready to use — Enabled and available for agents or chat (subject to Enable in Chat and tool selection).
- Needs setup — Still missing sign-in, an API key, or another configuration step before members can rely on it.
Use those labels to finish incomplete connections and avoid enabling a connector that is not ready for your team.
Connection mode (personal vs shared)
Where a connector supports it, choose how accounts connect:
- Each person connects their own account — Members authorize access individually (typical for OAuth). Best when people should only see their own data.
- One connection for everyone — The organization shares a single connection. This is useful when the whole team should work against the same shared system or service account.
Follow the labels in the product for the connector you are configuring; not every integration offers both modes.
Enabling and disabling
Each connector has two toggle controls:
- Enabled — Controls whether the connector is active for the organization. When disabled, no agents can use it.
- Enable in Chat — Controls whether the connector is available during agent chat sessions. When enabled, a chat tool is created and agents can actively use the connector's tools.
Editing a connector
Click Edit on any connector to update its authentication credentials, URL, or selected tools.
Deleting a connector
Click Delete to remove a connector. This disconnects it from all agents that were using it.
Selecting tools
For both pre-built and custom connectors, you can control which tools are available to agents. Each tool represents a specific capability (such as reading messages, creating issues, or listing files). Deselecting tools you do not need helps keep agent behavior focused and reduces unnecessary API calls.
📝 Note: Each MCP server connection supports up to 100 selected tools.
Tool permission groups
Tool permissions are grouped so you can enable or disable a whole category, then refine individual tools:
| Group | Meaning |
|---|---|
| Read | View and search information without changing it. |
| Write | Create or send data; not marked destructive by the provider. |
| Delete or overwrite | Remove or replace existing data; marked destructive by the provider. |
| Unclassified | The provider has not supplied enough access information—review these tools individually. |
You can still open individual tools, including unclassified ones, and turn them on or off one at a time.
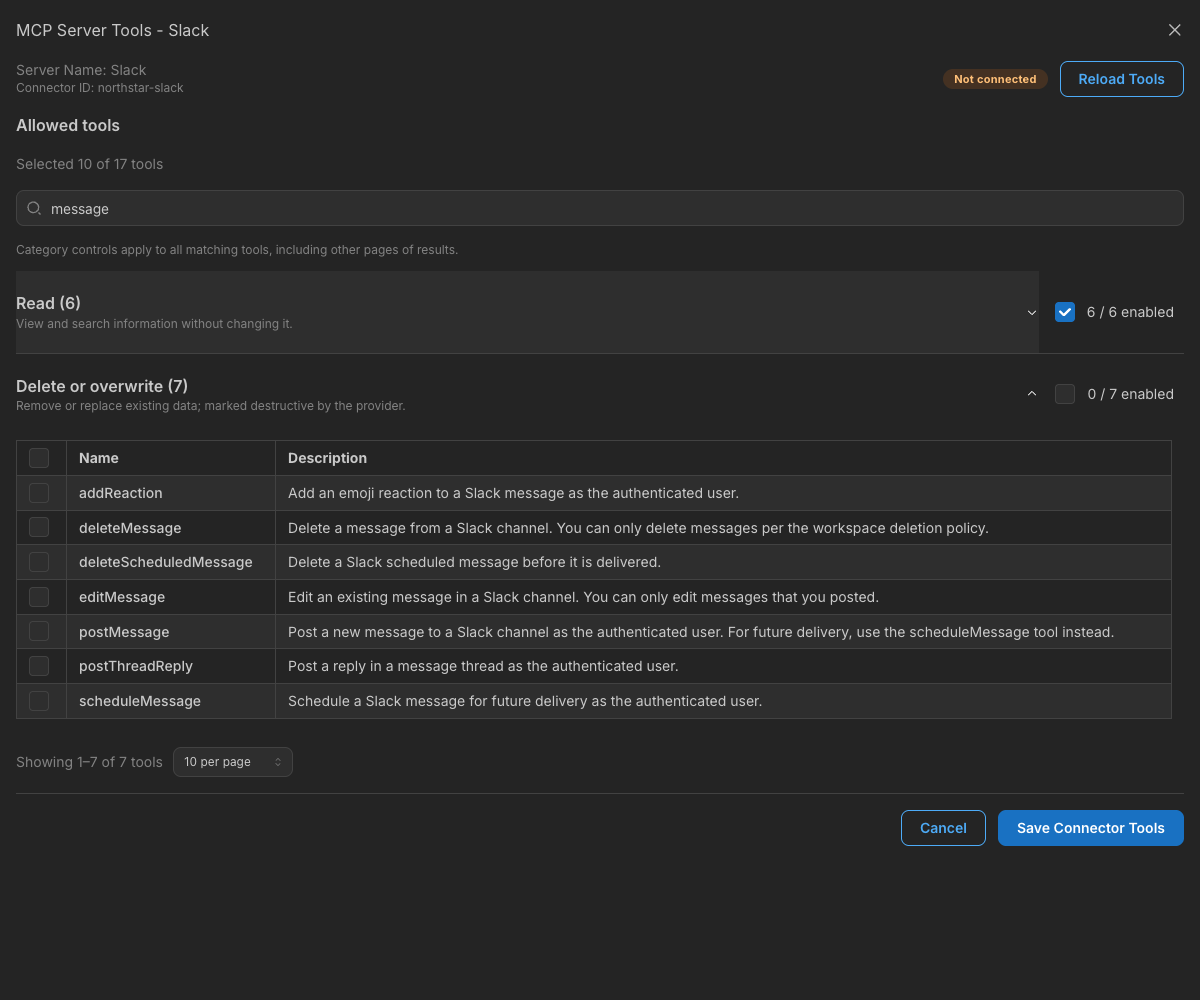
Example: review tools by category (such as Read or Delete or overwrite), then enable or disable individual tools before you save. Sample data in the screenshot may differ from your organization.
Member reconnect and disconnect
In account settings, connector cards provide clearer status plus Disconnect and Reconnect so members can refresh an expired or broken personal connection without waiting on an admin for every case. Organization-level enablement and Enable in Chat still control whether the connector is available at all.
Discover connectors from chat
When connector discovery is enabled for your organization, default chat can search for a relevant connector even if it is not enabled yet.
- Admins may see a card to Enable, Install, or Finish setup for the organization (or Enable in chat when the connector is already installed but not turned on for your selection).
- Members who cannot change org setup see guidance to ask an admin (For connectors that need organization setup, ask your admin…).
- Badges such as Not enabled or Setup needed show what is blocking use.
- When a relevant connection is already available, chat prefers that connector for supported tasks instead of navigating the same service through the browser.
- A connector your organization has configured but you have not selected can appear with Enable in chat (member selection for the next message—complete sign-in if needed). This is separate from the org-level Enable in Chat toggle on the Connectors page. The connector picker supports category filtering alongside search.
- Saved-agent chats continue to use the tools configured for that agent, not the ad hoc chat picker selection.
Members still cannot adopt a vendor for the whole organization from chat alone. Organization-wide install and shared credentials stay in Organization → Connectors.
Security
- OAuth tokens and API keys are encrypted at rest using AES-256-GCM encryption.
- OAuth tokens are stored per-user — each user's authorization is independent.
- Credentials are never exposed in the admin UI after they are saved.
- Pass-through headers exist only for the duration of the request and are never stored.
- MCP tool calls are executed with additional safeguards (for example, stronger handling of server-side request risks) so a misbehaving remote server is less likely to abuse the integration.
- OAuth-based MCP tools cannot be used in the standard embeddable widget. Use API key or pass-through header auth for agents you plan to embed.
Next steps
Once your organization has MCP servers configured, agent creators can connect them to individual agents. See Configuring extended capabilities for instructions on linking MCP servers to agents and selecting which tools each agent can use.